The Origins of the Kill Chain
The US Air Force breaks a strike into six phases, known as F2T2EA. In 2010, Lockheed Martin carried the idea over into cybersecurity, proposing the Cyber Kill Chain and trademarking it, much to Jeffrey Carr's displeasure. Mandiant's eight-stage APT model took off on the back of its Unit 61398 report, while Gartner went its own way. Along the way, a look at why the cyber kill chain suits defense in depth inside the internal network, and why it is so hard to put into practice.
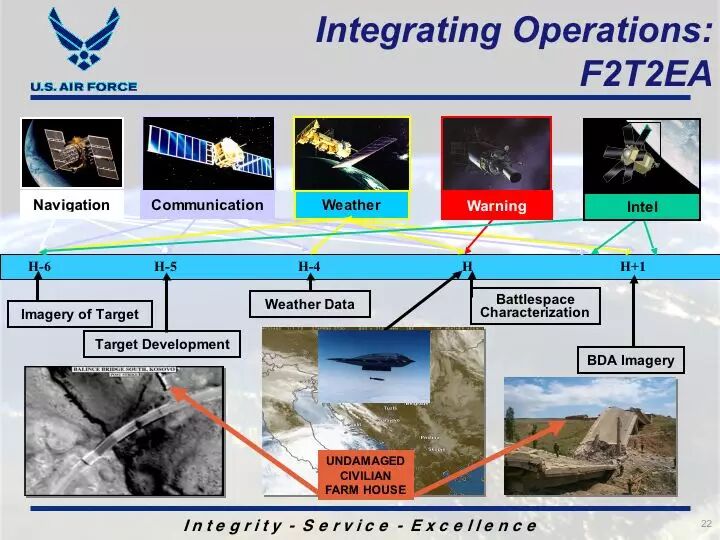
美国空军为了便于描述和指挥,将一次进攻分为不同的阶段,如:
搜寻Find
锁定Fix
跟踪Track
定位Target
打击Engage
评估Assess
简称F2T2EA,这种分阶段描述进攻的模型称为Kill Chain,这里我翻译为“攻击链”。
洛克希德马丁公司是美国空军的主要供应商之一,对空军的套路、术语很熟悉;同时,他们对自身的网络安全非常重视。2010年,洛马公司将美国空军的方法论引入到网络安全领域,提出一个叫做“Cyber Kill Chain”的模型(1),并注册了商标。Cyber Kill Chain我翻译为“网络攻击链”。这一模型将入侵者对网络的攻击也分为不同的阶段,如:
探测(目标的各种信息)Reconnaissance
准备(攻击手段和工具)Weaponization
投放(攻击载荷)Delivery
利用(受害者机器执行恶意代码)Exploit
安装(木马后门)Installation
(远程)控制Command & Control
执行(目标行动)Actions
也有一种说法是,Cyber Kill Chain是网络安全专家Jeffrey Carr在2008年提出的。维基百科上介绍说,Jeffrey Carr为俄国和中国的“网络战”做过战略咨询。听过洛马公司注册了Cyber Kill Chain的商标,Jeffrey Carr在自己的博客上表达了不满(2)。
2010年,Mandiant公司也提出过一个网络攻击周期模型。这家公司是APT概念的提出者(3)。RSA2013会议前夕,2013年2月19日,Mandiant公司公布了一份指责中国军方黑客袭击美国141家企业的细节追踪报告(4),暴露了驻扎在上海的中国网军61398部队,引起轩然大波。自此,APT的概念大热。2013年12月30日,以检测和防止APT著称FireEye上市仅三个月,就以10亿美元收购了Mandiant公司。也算是投桃报李吧。
Mandiant公司在2010年提出APT概念时将攻击分为8个阶段:
探测目标reconnaissance
初始侵入initial compromise
建立落脚点establish a foothold
提升权限escalate privileges
内部侦查internal reconnaissance
横向发展move laterally
保持存在maintain a presence
完成任务complete the mission
显然,这个模型比洛马公司的CKC复杂,多了点书生气。比较适合用来描述APT,通用性不强。
在这个行业术语、概念和事实的工业标准之争中,怎么少得了Gartner。洛马注册了商标,起晚了的Garter当然要另起炉灶——他们用的术语是CyberAttack Chain(5)。前面我已经把CyberKill Chain翻译为网络攻击链的情况下,这个CAC只能也翻译为“网络攻击链”了。没关系,反正是一回事儿。
CKC也罢,CAC也罢,这个“网络攻击链”模型如何?怎么用?
说起来话还长。简单地说,这个模型注重早期防护与和主动防御,结合大数据技术,可以进行基于语义的攻击检测,能力超越传统的基于语法的攻击检测技术,非常适合复杂的IT架构,如大型内部专网、云计算架构等,进行内部的纵深防御,特别是防御多阶段、跨网络跨设备、长时间多事件的高级、复杂的攻击行为。
但是,真要参照这样的模型进行部署,提高内网攻击检测和防护能力,不是那么简单的事。以后再详说。
题图为美国空军进攻基地组织的无人机。
(1)
(2)
http://jeffreycarr.blogspot.com/2013/08/the-cyber-kill-chain-trademarked-by.html
(3) M-Trends: The Advanced Persistent Threat.
https://www.mandiant.com/resources/mandiant-reports/
(4) APT1: Exposing One of China’s Cyber Espionage Units
http://intelreport.mandiant.com/Mandiant_APT1_Report.pdf
中文版:
http://www.valleytalk.org/wp-content/uploads/2014/05/Mandiant报告:揭秘一支中国网络间谍部队.pdf
注
- (5) SelectingSecurity Monitoring Approaches by Using the Attack Chain Model
Originally published on the WeChat account 网安志异, 2015-06-29 · original
Comments